On this page · 11 sections
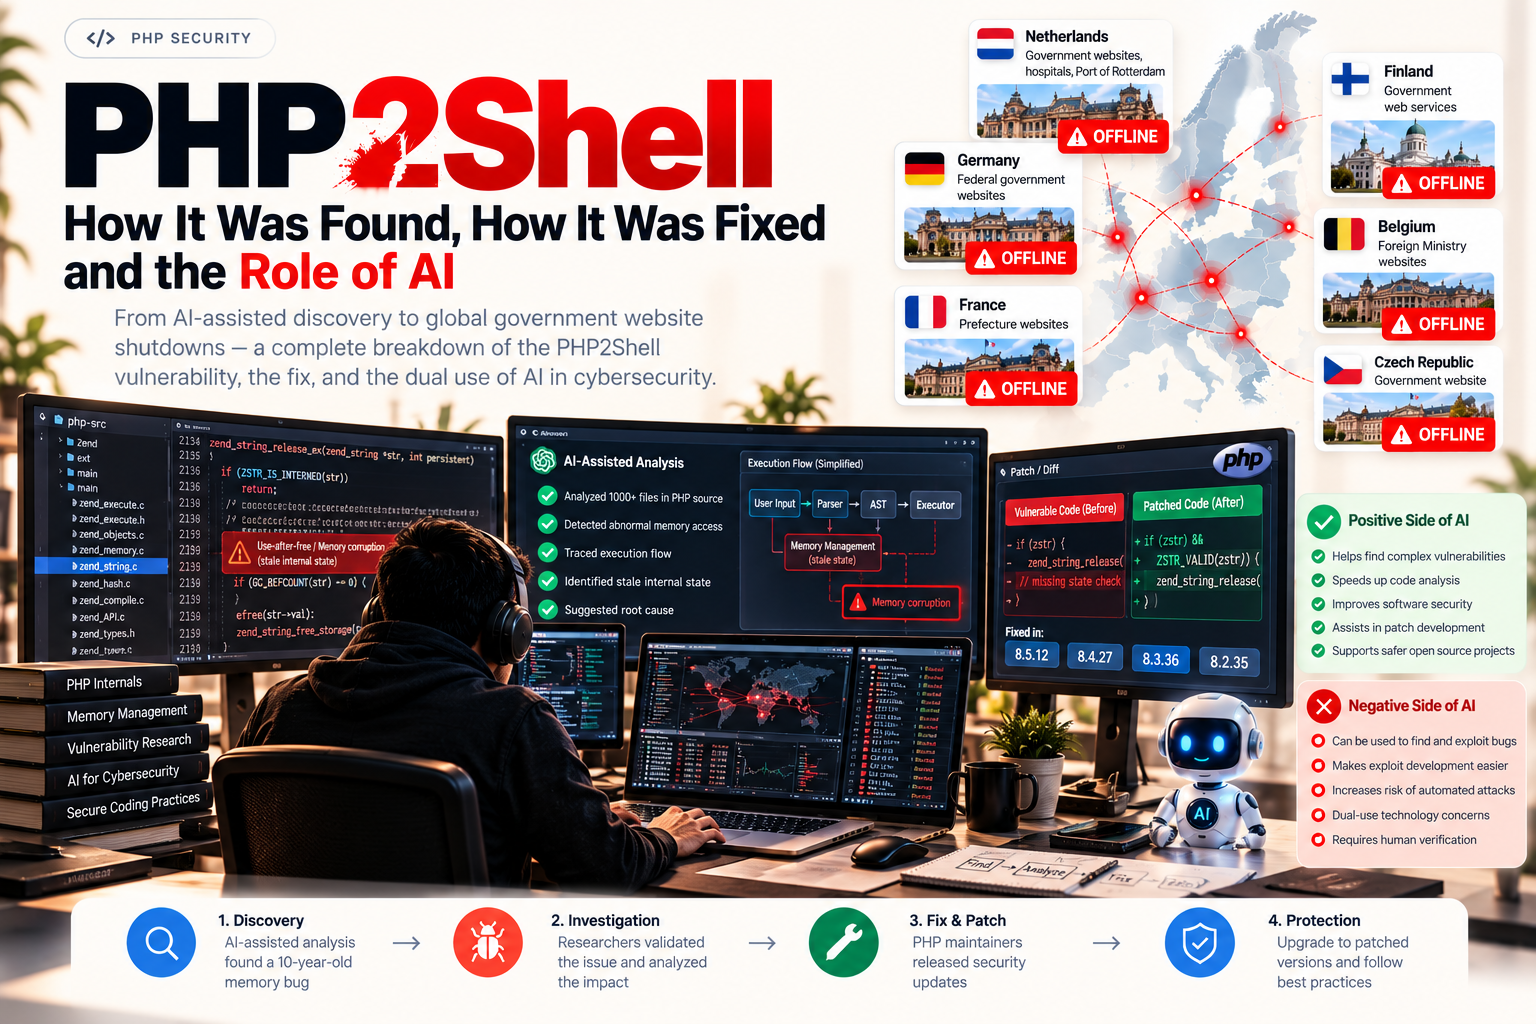
Summary. PHP2Shell, the pair of critical PHP flaws fixed on 21 October 2026 (CVE-2026-109618 and CVE-2026-109619, both CVSS v4.0 9.2), was found by human researchers using AI, not by AI alone. Calif's Ryan Austin surfaced the first out-of-memory bug on 1 August, a few days into an audit run under OpenAI's Patch the Planet programme, and OpenAI says he used GPT-5.6 Sol; Calif's own write-up credits an LLM companion and names no model. Wiz found the flaws independently from 19 August using Wiz Atlas, Gemini 4 Argon and GPT-5.6 Sol. The bug had a long trail: a 2020 report that looked harmless and a 2024 Quarkslab audit that spotted the out-of-memory problem without proving it exploitable. PHP's fix, a single commit, stops out-of-memory errors from jumping out of half-finished operations and resets request state between requests. The same AI that sped up discovery also speeds up attackers: Wiz warns that AI makes complex exploits easier to adapt, and exploitation reports followed within a day of disclosure. Patch PHP first; the lessons about AI come second.
About this article. Facts were checked against PHP's advisories and source commits, the PHP Foundation, Calif's and Wiz's write-ups, Datadog Security Labs and press reports quoting OpenAI on 22 October 2026. OpenAI's own post blocks automated readers, so its claims are attributed through Fortune. This article explains the vulnerabilities at a high level and gives no exploit procedure. Researched with AI assistance and reviewed by our editorial team.
Quick summary
- What: two memory-safety flaws in PHP's core runtime, known together as PHP2Shell.
- Impact: unauthenticated remote code execution as the web worker account; CVE-2026-109619 can also disclose memory.
- How it was found: researchers at Calif and Wiz, working separately, used AI tools inside targeted investigations, then validated every result by hand.
- How it was fixed: PHP replaced the way it bails out on memory exhaustion and resets leftover request state.
- What to do: update to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35, or your vendor's patched package. Our PHP2Shell fix guide walks through it.
What PHP2Shell is
PHP2Shell is two bugs in php-src, the engine underneath WordPress, Drupal, Joomla and most PHP applications, so updating a CMS does not fix it. Both turn an error that interrupts PHP mid-operation into a way to corrupt or reuse memory.
| Vulnerability | PHP's title | What goes wrong | Stated impact |
|---|---|---|---|
| CVE-2026-109618 | RCE via OOM corruption | An out-of-memory error can leave request memory uninitialised, and the cleanup that follows reads or acts on it | Unauthenticated remote code execution |
| CVE-2026-109619 | RCE via stale global state | Global state can keep pointing at request memory after it is freed, so a later request reads stale data | Heap use-after-free, memory disclosure and remote code execution |
Both score 9.2 under CVSS v4.0, and PHP's GitHub advisories for CVE-2026-109618 and CVE-2026-109619 give the detail. PHP rates Apache's mod_php as the highest-risk setup, because a demonstrated exploit fires before any application code runs. For the wider fallout, including the government sites taken offline across Europe, see our PHP2Shell news explainer.
How the bug was found
A long trail of clues
Calif's write-up traces the idea back to 2004, when researcher Stefan Esser published the first PHP memory-limit remote vulnerability. A 2020 PHP bug report on the same theme looked harmless. In 2024, an OSTIF-organised audit by Quarkslab, funded by Germany's Sovereign Tech Agency, rediscovered the out-of-memory issue; a developer contracted by the PHP Foundation found the first signs while fixing an audit finding, but no concrete exploit was found.
Spotting a suspicious crash and proving it is exploitable are different jobs. PHP2Shell sat in the gap between them for years.
Calif and Patch the Planet
Patch the Planet is OpenAI's programme pairing AI-assisted vulnerability research with open-source maintainers. Calif began its PHP audit on 30 July 2026 after OpenAI invited it to join, and the PHP Foundation says it helped bring PHP into the programme.
Austin went back to the memory-limit history and asked his LLM companion for help exploring it. Within a few days, on 1 August, the team surfaced the first exploitable out-of-memory fatal error. OpenAI told Fortune that Calif used GPT-5.6 Sol. Calif itself names no model, says it used no harness or models that were not generally available, and warns that no model can unearth every bug from simple prompts: knowing your target still matters.
Wiz in parallel
Wiz Research found the flaws on its own. Its write-up says it used Wiz Atlas, Gemini 4 Argon and GPT-5.6 Sol throughout, with Gemini 4 Argon making the largest contribution to finding the bug, building the exploit, detecting attacks and validating the patch. Wiz confirmed unauthenticated remote code execution against Drupal on 20 August and WordPress on 21 August, later showed it on Joomla too, and published no exploit code.
What AI did, and what people did
Across both accounts, AI helped researchers read a large legacy codebase, explore hypotheses about memory state, reason about which paths might be reachable, and iterate on proofs of concept. People chose the target and the historical bug pattern worth revisiting, judged which suggestions made sense, built and checked reproductions, and reported through PHP's security process. The useful lesson is not that AI found a bug by itself, but that experienced researchers with AI in a disciplined workflow found a hard bug faster.
Timeline: from first clue to public fix
| Date | Milestone |
|---|---|
| 2020 | A memory-limit issue reported to PHP looks harmless |
| 2024 | Quarkslab audit rediscovers the out-of-memory issue; exploitability not proven |
| 30 July 2026 | Calif starts its PHP audit under Patch the Planet |
| 1 August | Calif surfaces the first exploitable out-of-memory fatal error |
| 11 August | Calif reports the first bug; the PHP Foundation says OpenAI reported the same root cause that day |
| 14 to 15 August | Calif shares a remote code execution proof of concept and PHP confirms it works |
| 19 to 24 August | Wiz discovers the flaws, confirms RCE on Drupal and WordPress, and reports to PHP |
| 21 August | Calif reports the second bug |
| 18 September | OpenAI reports further attack vectors, per the PHP Foundation |
| 20 October | The CVE identifiers leak and Calif mistakenly publishes a proof-of-concept video |
| 21 October | PHP releases fixes and the flaws are disclosed |
Accounts differ on one point. Wiz's timeline says PHP acknowledged its reports and began a coordinated fix on 21 September, while the PHP Foundation says fixing became its top priority from 11 August and calls the two-month gap a structural failure it is now addressing.
How PHP fixed it
The fix is a single commit, which PHP describes as avoiding state corruption via bailout, applied to every supported branch. It does two things.
It changes what happens when PHP runs out of memory. Previously, hitting memory_limit made PHP jump straight out of whatever it was doing, which could leave half-built structures for cleanup code to trip over. Now exceeding the limit raises a deferred fatal error at the next safe point in the engine. If memory keeps climbing past a second, higher threshold, PHP ends the worker immediately and skips cleanup entirely. That hard limit is set by a new memory_hard_limit_percent setting, which by default allows twice the memory_limit, or memory_limit plus 1 GB for limits of 1 GB and above.
It resets request state that could go stale. At shutdown PHP now clears error and exception state, and before early request processing it initialises serialisation and session state, so one interrupted request cannot hand a dangling pointer to the next. Datadog Security Labs' analysis walks through both changes and the detection signals that follow from them.
PHP shipped the fix in 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and published minimal source backports for 7.4, 8.0 and 8.1 as git branches rather than releases. Its advisory says the interim configuration measures it lists reduce exposure to specific attack paths but do not make an installation safe.
What the PHP Foundation is changing
The PHP Foundation used its disclosure post to describe how it is responding:
- People. It set up an Ecosystem Security Team in May 2026, including an AI security engineer in residence, and has added staff since.
- AI tooling with humans in charge. It has scanned PHP with Anthropic's Claude Mythos, working with Alpha-Omega, and uses OpenAI's Daybreak Red to validate reports and exploits. Its rule is that "a person makes every call and works on every patch".
- Process and money. It is changing its security process so decisions can be made by majority, and asks companies, hosts and governments to fund the work.
The positive side of AI in security
Finding patterns in large, old codebases. PHP is three decades of C. AI helped researchers revisit a historical bug class, follow call paths and keep pushing past an unexplained crash.
Making specialists more productive. Hypotheses, code explanations and test ideas came faster, leaving experts more time to validate impact and help with a reliable fix.
Giving defenders a head start. The flaws were reported privately, and PHP and partners such as Cloudflare had time to prepare fixes and firewall rules before disclosure. The leak on 20 October shortened that window, but it still existed.
Reaching under-resourced projects. Open-source projects with many users and small security teams are where AI-assisted auditing could help most, provided there are funded people to review and ship fixes.
The negative side: AI speeds up attackers too
Lower barriers to exploitation. Wiz warns that as AI reduces the effort needed to develop and adapt complex exploits, vulnerabilities that once looked impractical become viable targets, and that LLMs can help adapt an exploit to different PHP versions, configurations and memory layouts.
Faster weaponisation. Within a day of disclosure, New Zealand's NCSC said it was aware of reports of active exploitation, and Datadog cites AWS seeing attempts as early as 17 October. Our guide to AI-assisted cyberattacks covers what that speed means for defenders.
Quiet compromises. Datadog notes that a successful exploit does not necessarily crash the worker or return an error, so defenders cannot rely on outages to tell them something happened.
False confidence. AI can produce plausible but wrong explanations, or a fix that covers one path and misses another. Here, every finding was reproduced by people and the patch was written by PHP's maintainers.
Disclosure discipline. The leaked identifiers and the accidental video show that coordinated disclosure is fragile even when everyone means well. AI-generated proof-of-concept code is still dangerous code.
So, is AI good or bad for security?
Neither, on its own. PHP2Shell shows the same capability working on both sides: researchers used AI to dig up an old flaw and give maintainers time to fix it, and attackers can use comparable tools to understand the patch and adapt an exploit. What decides the outcome is access, human review, responsible disclosure and how fast the ecosystem patches. If you run AI coding or review tools yourself, our comparison of AI security scanners in CI and our guide to autonomous patching are useful next reads.
How eCorpIT can help
eCorpIT is a Gurugram-based technology organisation, founded in 2021, assessed at CMMI Level 5 and MSME certified, with senior-led engineering teams working across AWS, Microsoft and Google platforms. Our secure AI-assisted development service adds AI-assisted code review with human validation to your delivery pipeline, and our PHP development team can patch and upgrade PHP runtimes across your estate. Talk to us at /contact-us/.
Last updated: 22 October 2026.